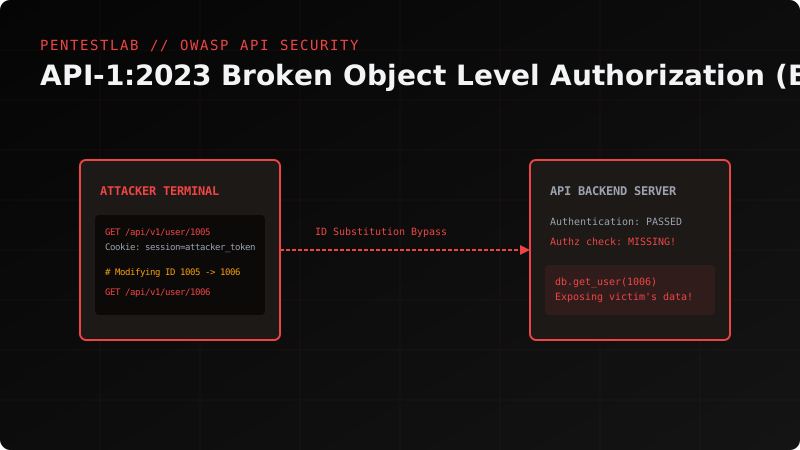
The integration of microservices, mobile apps, and Single Page Applications (SPAs) has shifted the focus of modern web development entirely to APIs. Today, APIs serve more than 80% of all public web traffic. However, traditional Web Application Firewalls (WAFs) are often blind to API logic attacks, as a malicious actor's payload format looks perfectly valid under standard HTTP parsing rules.