vulnerability analysis

2 posts

Many modern web platforms provide features to export system data into PDF formats, such as billing invoices, accounting reports, and resumes. Behind the scenes, these document engines usually share a common architecture: they accept HTML code (or compile it from an application template) and render it into a PDF file using specialized libraries like **wkhtmltopdf**, **WeasyPrint**, **dompdf**, or headless browser instances like **headless Chrome (Puppeteer / Playwright)**.
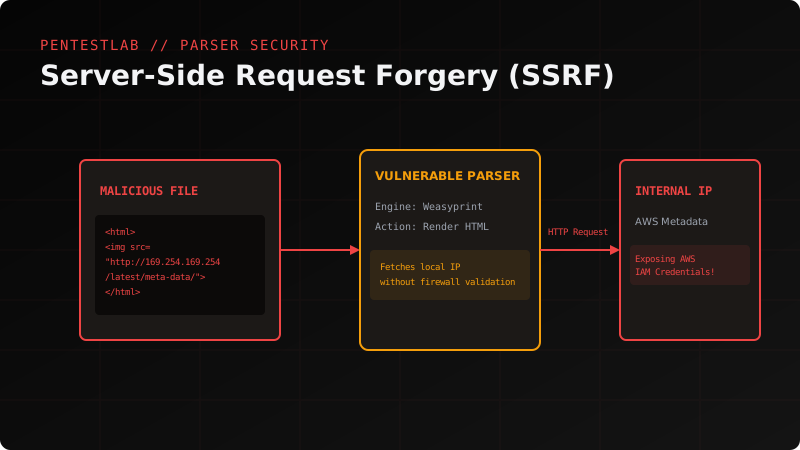
SSRF Vulnerabilities in Document and PDF Parsers: Exploitation and Defense
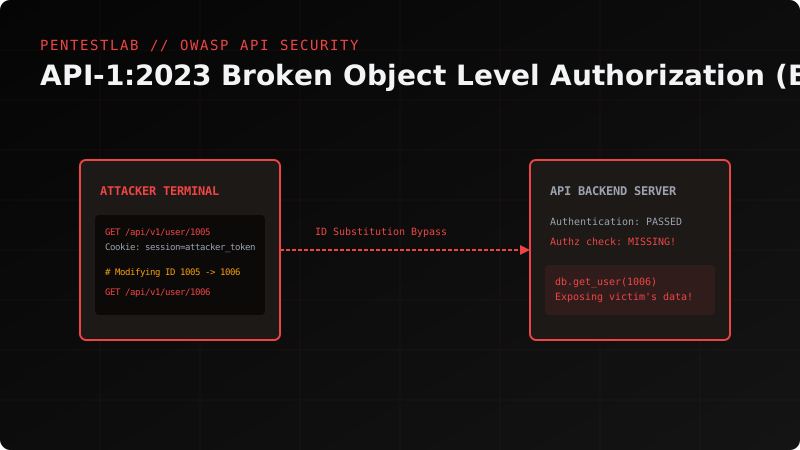
The integration of microservices, mobile apps, and Single Page Applications (SPAs) has shifted the focus of modern web development entirely to APIs. Today, APIs serve more than 80% of all public web traffic. However, traditional Web Application Firewalls (WAFs) are often blind to API logic attacks, as a malicious actor's payload format looks perfectly valid under standard HTTP parsing rules.
Deep Dive into the OWASP API Security Top 10 Standard with Practical Examples