Posts tagged with #owasp

4 posts

The integration of microservices, mobile apps, and Single Page Applications (SPAs) has shifted the focus of modern web development entirely to APIs. Today, APIs serve more than 80% of all public web traffic. However, traditional Web Application Firewalls (WAFs) are often blind to API logic attacks, as a malicious actor's payload format looks perfectly valid under standard HTTP parsing rules.
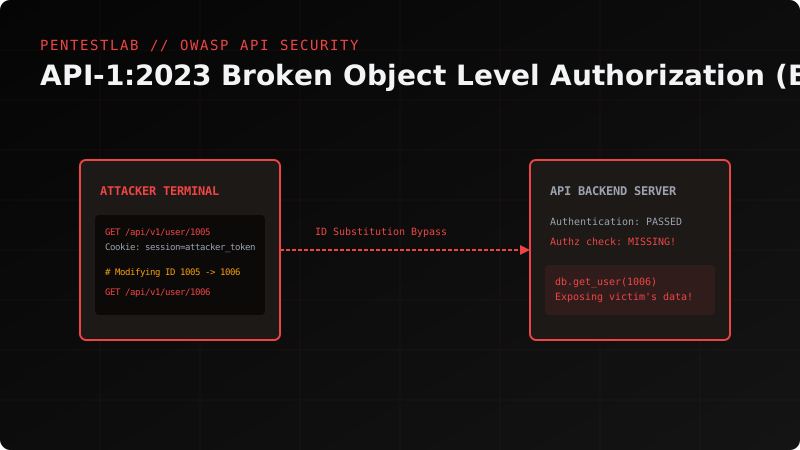
Deep Dive into the OWASP API Security Top 10 Standard with Practical Examples
In modern cybersecurity, defending a network requires thinking exactly like an attacker. Penetration testing is the structured simulation of cyberattacks against an enterprise's defense perimeter to identify structural flaws before malicious actors do. ## The OWASP Top 10 Framework Every professional security assessment should start with the **OWASP Top 10**, representing the most critical security risks to web applications:
Modern Penetration Testing: Identifying Vulnerabilities and Exploits
In the rapidly evolving landscape of modern systems and digital applications, achieving top-tier performance, security, and scalability is no longer optional. This article provides a comprehensive, technically rigorous analysis of current industry standards, exploring architectural paradigms, concrete code patterns, and practical execution checklists to harden and optimize your production systems.
Exploiting and Mitigating JWT Signature Bypass Vulnerabilities
In the rapidly evolving landscape of modern systems and digital applications, achieving top-tier performance, security, and scalability is no longer optional. This article provides a comprehensive, technically rigorous analysis of current industry standards, exploring architectural paradigms, concrete code patterns, and practical execution checklists to harden and optimize your production systems.
Advanced SQL Injection Vectors in Modern Object-Relational Mappers